The Internet

India Shuts Down Internet Once Again, This Time In Assam and Meghalaya (techcrunch.com) 66

An anonymous reader quotes a report from TechCrunch: India maintained a shutdown of the internet in the states of Assam and Meghalaya on Friday, now into 36 hours, to control protests over a controversial and far-reaching new citizen rule. The shutdown of the internet in Assam and Meghalaya, home to more than 32 million people, is the latest example of a worrying worldwide trend employed by various governments: preventing people from communicating on the web and accessing information.

On Thursday, India's president Ram Nath Kovind approved the Citizenship Amendment Bill, a day after the country's Parliament passed it. The law offers a path to Indian citizenship for non-Muslim minorities from three neighboring countries (Afghanistan, Pakistan and Bangladesh) -- not for the country's own Muslim minority. Shortly after the bill was passed, protests broke out in the streets in the northeastern states of Assam and Meghalaya, where residents have long been concerned about immigration from the aforementioned nations. In Meghalaya, texting services have been suspended, too. To contain the situation, the Indian government sent in troops and shut down the internet -- a measure that the United Nations has condemned in the past, calling it a violation of human rights.

Facebook

Someone Stole Facebook Payroll Data For Thousands of Employees (bloomberg.com) 29

mschaffer writes: Apparently Facebook had a recent privacy problem of a different kind. A thief broke into an employee's car and stole equipment -- including hard drives that contained unencrypted personal data of former Facebook employees. "Out of abundance of caution," Facebook alerted their current and former employees about the theft. "The hard drives, which were unencrypted, included payroll data like employee names, bank account numbers and the last four digits of employees' social security numbers," reports Bloomberg. "The drives also included compensation information, including salaries, bonus amounts, and some equity details. In total, the drives contained personal data for about 29,000 U.S. employees who worked at Facebook in 2018."

"We worked with law enforcement as they investigated a recent car break-in and theft of an employee's bag containing company equipment with employee payroll information stored on it," the spokeswoman said in a statement shared with Bloomberg. "We have seen no evidence of abuse and believe this was a smash and grab crime rather than an attempt to steal employee information."
Security

New Orleans City Government Shuts Off Computers After Cyberattack (nola.com) 30

New submitter tubajock writes: According to NOLA.com, New Orleans City Hall workers were told by a PA system broadcast to immediately unplug all computer systems from the network [following a cyberattack that struck the city government]. The city website is also down and the city has implemented its Emergency Operations Center as well as contacted state and federal authorities for help. Beau Tidwell, a spokesman for Mayor LaToya Cantrell, said the cyberattack started sometime after 11 a.m. In addition to city hall workers, the New Orleans Police Department has also been told to shut down their computers and remove everything from the network.

Thankfully, 9-1-1 and 3-1-1 calls are not impacted by the attack and residents can still access the online 3-1-1 systems through its site, nola311.org.
AT&T

AT&T Drops Out of FCC Speed-Test Program So It Can Hide Bad Results 53

An anonymous reader quotes a report from Ars Technica: AT&T doesn't want its home Internet speeds to be measured by the Federal Communications Commission anymore, and it already convinced the FCC to exclude its worst speed-test results from an annual government report. "AT&T this year told the commission it will no longer cooperate with the FCC's SamKnows speed test," The Wall Street Journal wrote in an investigative report titled "Your Internet provider likely juiced its official speed scores." AT&T already convinced the FCC to exclude certain DSL test results from last year's Measuring Broadband America report. The reports are based on the SamKnows testing equipment installed in thousands of homes across the U.S.

"AT&T was dismayed at its report card from a government test measuring Internet speeds" and thus "pushed the Federal Communications Commission to omit unflattering data on its DSL Internet service from the report," the Journal wrote. "In the end, the DSL data was left out of the report released late last year, to the chagrin of some agency officials," the Journal wrote. "AT&T's remaining speed tiers notched high marks."
"AT&T developed a best-in-class tool to measure its consumer broadband services," the company said in a statement provided to Ars. "This tool measures performance on all AT&T IP broadband technologies and is more accurate, versatile, and transparent. For these and other reasons, our tool provides better and more useful information to our customers."
Security

Mozilla To Force All Add-on Devs To Use 2FA To Prevent Supply-Chain Attacks (zdnet.com) 21

Mozilla announced this week that all developers of Firefox add-ons must enable a two-factor authentication (2FA) solution for their account. From a report: "Starting in early 2020, extension developers will be required to have 2FA enabled on AMO [the Mozilla Add-Ons portal]," said Caitlin Neiman, Add-ons Community Manager at Mozilla. "This is intended to help prevent malicious actors from taking control of legitimate add-ons and their users," Neiman added. When this happens, hackers can use the developers' compromised accounts to ship tainted add-on updates to Firefox users. Since Firefox add-ons have a pretty privileged position inside the browser, an attacker can use a compromised add-on to steal passwords, authentication/session cookies, spy on a user's browsing habits, or redirect users to phishing pages or malware download sites. These types of incidents are usually referred to as supply-chain attacks.
The Courts

Lawsuit Forces CenturyLink To Stop Charging 'Internet Cost Recovery Fee' (arstechnica.com) 43

CenturyLink has agreed to pay a $6.1 million penalty after Washington state regulators found that the company failed to disclose fees that raised actual prices well above the advertised rates. CenturyLink must also stop charging a so-called "Internet Cost Recovery Fee" in the state, although customers may end up paying the fee until their contracts expire unless they take action to switch plans. Ars Technica reports: "CenturyLink deceived consumers by telling them they would pay one price and then charging them more," Washington Attorney General Bob Ferguson said in an announcement yesterday. "Companies must clearly disclose all added fees and charges to Washingtonians." Ferguson encouraged Washington residents "who believe they have received bills that include undisclosed fees to file a complaint" with the state. Ferguson's office said it began investigating CenturyLink in 2016 "after receiving complaints from consumers that their actual bills were more than the advertised price, or the price that they were promised by sales representatives."

Here's what Ferguson's office found: "There were three main fees CenturyLink did not disclose: a broadcast fee of $2.49 per month, a sports fee of $2.49 per month, and CenturyLink's 'Internet Cost Recovery Fee,' ranging from $0.99 to $1.99 per month. CenturyLink charged its Internet Cost Recovery Fee to 650,000 Washingtonians. Of those, another 60,000 were also charged the broadcast and sports fees. These fees alone added up to $7 per month to a television subscriber's bill -- $84 per year. The investigation found that CenturyLink did not adequately disclose additional taxes and fees for its cable, Internet and telephone services." CenturyLink admitted no wrongdoing but agreed to a financial settlement and changes in business practices as part of a consent decree filed in King County Superior Court on Monday. The attorney general's office detailed its allegations in a lawsuit filed the same day.

Google

Google Hands Feds 1,500 Phone Locations In Unprecedented 'Geofence' Search (forbes.com) 53

According to Forbes, Google has sent 1,494 device identifiers to the Bureau of Alcohol, Tobacco, Firearms and Explosives (ATF) to help them investigate arsons carried out across Milwaukee, Wisconsin, throughout 2018 and 2019. "The requests, outlined in two search warrants obtained by Forbes, demanded to know which specific Google customers were located in areas covering 29,387 square meters (or 3 hectares) during a total of nine hours for the four separate incidents," the report says. "Unbeknownst to many Google users, if they have 'location history' turned on, their whereabouts are stored by the tech giant in a database called SensorVault." From the report: To investigators, this kind of "geofence" demand is useful, allowing them to go through the data trove provided by Google, look for devices of interest such as a known suspect's phone and ask for more personal information on the user of that mobile. But it's also the kind of search that's been making pro-privacy folk anxious over the last year. Such data grabs, also referred to as "reverse location searches," see the police give Google a timeframe and an area on Google Maps within which to find every Google user within. Google then looks through its SensorVault database of user locations, taken from devices running the tech giant's services like Google Maps or anything that requires the "location history" feature be turned on. The police then look through the list, decide which devices are of interest to the investigation and ask for subscriber information that includes more detailed data such as name, email address, when they signed up to Google services and which ones they used.

It's unclear whether or not Google handed over any identifying information, but to Jerome Greco, a public defender in the Digital Forensics Unit of the Legal Aid Society, it's a sign that geofence warrants are overly broad and endanger user privacy. "The number of phones identified in that area shows two key points," he tells Forbes. "One, it demonstrates a sample of how many people's minute-by-minute movements Google is precisely tracking. "Two, it shows the unconstitutional nature of reverse location search warrants because they inherently invade the privacy of numerous people, who everyone agrees are unconnected to the crime being investigated, for the mere possibility that it may help identify a suspect."
For what it's worth, Forbes did obtain a search warrant that indicates Google is trying to fight back against overly broad government requests, "but still appears to be handing over innocent people's information as well as legitimate suspect data."
Government

988 Will Be the New 911 For Suicide Prevention (arstechnica.com) 66

An anonymous reader quotes a report from Ars Technica: The Federal Communications Commission plans to designate 988 as the short dialing code for the United States' suicide-prevention hotline. Much like 911 for general emergencies, 988 could be dialed by anyone undergoing a mental health crisis and/or considering suicide. The National Suicide Prevention Lifeline can already be reached at 1-800-273-8255 (or 1-800-273-TALK), but the FCC today gave preliminary approval to a plan that would make 988 redirect to that hotline. The commission's unanimous vote approved a Notice of Proposed Rulemaking (NPRM) that seeks public comment on the plan.

Once the NPRM is published in the Federal Register, there will be a 60-day period for taking public comments, and the FCC would finalize the plan after considering the public input. It could take another 18 months after that to implement 988 nationwide, depending on what requirements the FCC imposes on phone providers. [...] The proposal would require all telecommunications carriers and interconnected VoIP providers to support 988 on their networks within 18 months, the FCC said. But the FCC noted that it is "seek[ing] comment on all aspects of implementation, including whether a longer or shorter timeframe would be needed to make 988 a reality." Based on the comment-period length and proposed implementation time frame, 988 would be implemented nationwide sometime in late 2021.

Facebook

FTC May Try To Delay Facebook's Plan To Integrate its Apps (cnn.com) 9

Facebook's stock took a dive on Thursday following a report that federal regulators may seek to prevent the company from more tightly integrating its social media products. From a report: The Federal Trade Commission is said to be considering asking for a court order to delay Facebook from making the services it owns, including WhatsApp, Instagram and Facebook Messenger, interoperable with one another, the Wall Street Journal reported, citing unnamed people familiar with the matter. Shares of Facebook fell more than 3 percent in afternoon trading Thursday after the news broke.
Privacy

Inside the Podcast that Hacks Ring Camera Owners Live on Air (vice.com) 112

In the NulledCast podcast hackers livestream the harassment of Ring camera owners after accessing their devices. Hundreds of people can listen. From a report: A blaring siren suddenly rips through the Ring camera, startling the Florida family inside their own home. "It's your boy Chance on Nulled," a voice says from the Ring camera, which a hacker has taken over. "How you doing? How you doing?" "Welcome to the NulledCast," the voice says. The NulledCast is a podcast livestreamed to Discord. It's a show in which hackers take over people's Ring and Nest smarthome cameras and use their speakers to talk to and harass their unsuspecting owners. In the example above, Chance blared noises and shouted racist comments at the Florida family. "Sit back and relax to over 45 minutes of entertainment," an advertisement for the podcast posted to a hacking forum called Nulled reads. "Join us as we go on completely random tangents such as; Ring & Nest Trolling, telling shelter owners we killed a kitten, Nulled drama, and more ridiculous topics. Be sure to join our Discord to watch the shows live."

Software to hack Ring cameras has recently become popular on the forum. The software churns through previously compromised email addresses and passwords to break into Ring cameras at scale. This has led to a recent spate of hacks that have occurred both during the podcast and at other times, several of which have been covered by local media outlets. In Brookhaven a hacker shouted at a sleeping woman through her hacked Ring camera to wake-up. In Texas, a hacker demanded a couple pay a bitcoin ransom. Hackers targeted a family in DeSoto County, Mississippi, and spoke through the device to one of the young children.

Security

Iran Banks Burned, Then Customer Accounts Were Exposed Online (nytimes.com) 47

The details of millions of Iranian bank cards were published online after antigovernment protests last month. Experts suspect a state-sponsored cyberattack. From a report: After demonstrators in Iran set fire to hundreds of bank branches last month in antigovernment protests, the authorities dealt with another less visible banking threat that is only now coming to fuller light: a security breach that exposed the information of millions of Iranian customer accounts. As of Tuesday, details of 15 million bank debit cards in Iran had been published on social media in the aftermath of the protests, unnerving customers and forcing the government to acknowledge a problem. The exposure represented the most serious banking security breach in Iran, according to Iranian media and a law firm representing some of the victims.

The breach, which targeted customers of Iran's three largest banks, was likely to further rattle an economy already reeling from the effects of American sanctions and came as Iran's leadership was grappling with deep-seated anger over its deadly crackdown on the protests. The number of affected accounts represents close to a fifth of the country's population. "This is the largest financial scam in Iran's history," reported Aftab News, a conservative media outlet. "Millions of Iranians are worried to find their names among the list of hacked accounts."

Crime

Genetic Database That Identified Golden State Killer Acquired By Crime Scene DNA Company (theverge.com) 39

"The crime scene DNA sequencing company Verogen announced yesterday that they've acquired the genomics database and website GEDmatch," reports The Verge. "GEDmatch was primarily used by genealogists until 2018, when police, the FBI, and a forensic genealogist identified the suspected Golden State Killer by tying crime scene DNA to relatives who had uploaded their genetic information to the site. Since then, the platform has helped identify around 70 people accused of violent crimes." From the report: The acquisition makes the relationship between the company and law enforcement explicit, but raises uncomfortable questions for users and experts about data privacy and the future direction of the platform. In response to privacy concerns, the company changed its terms and conditions last spring to only allow law enforcement access to data if users actively opted in. But until now, interaction with law enforcement was still a secondary function to the platform.

The announcement took many in the genetics and genealogy community by surprise, and many genealogists are leaving the platform. "There have simply been too many changes, all of them in the direction of making their data the product rather than the website a service," said lawyer and genealogist Judy Russell in an email to The Verge. GEDmatch users were prompted to accept new terms and conditions indicating the platform's new ownership, and could either agree and enter the site, or remove their data from the platform. Verogen will still allow users to keep their data from any use by law enforcement, CEO Brett Williams told BuzzFeed News, maintaining the opt-in approach. "It will be interesting to see in the future if the new owners will implement policy changes that will increase the number of individuals available for law enforcement searching," says James Hazel, postdoctoral fellow at the Center for Genetic Privacy and Identity in Community Settings at Vanderbilt University.
The report notes, however, that "opt-in is not a foolproof system for data protection." Last month, a Florida detective announced at a police convention that he had obtained a warrant to penetrate GEDmatch and search its full database of nearly one million users.
Printer

Ask Slashdot: Will We Ever Be Able To Make Our Own Computer Hardware At Home? 117

dryriver writes: The sheer extent of the data privacy catastrophe happening -- everything software/hardware potentially spies on us, and we don't get to see what is in the source code or circuit diagrams -- got me thinking about an intriguing possibility. Will it ever be possible to design and manufacture your own CPU, GPU, ASIC or RAM chip right in your own home? 3D printers already allow 3D objects to be printed at home that would previously have required an injection molding machine. Inkjet printers can do high DPI color printouts at home that would previously have required a printing press. Could this ever happen for making computer hardware? A compact home machine that can print out DIY electronic circuits right in your home or garage? Could this machine look a bit like a large inkjet printer, where you load the electronics equivalent of "premium glossy photo paper" into the printer, and out comes a printed, etched, or otherwise created integrated circuit that just needs some electricity to start working? If such a machine or "electronics printer" is technically feasible, would the powers that be ever allow us to own one?
The Courts

Netflix Ordered To Stop Poaching Fox Employees (variety.com) 96

A court on Tuesday issued an injunction barring Netflix from poaching employees from Fox and confirming the validity of fixed-term employment agreements. Variety reports: The ruling marks a hard-fought victory for Fox -- now owned by Disney -- which set out three years ago to stop Netflix from raiding its employees. Netflix had sought to invalidate Fox's fixed-term employment contracts, arguing that they locked employees into jobs they no longer wanted. Had Netflix prevailed, it would have upended a standard industry practice and given employees greater leverage in negotiations with their employers.

Santa Monica Superior Court Judge Marc Gross issued a tentative ruling on Nov. 25 indicating how he was likely to rule in the case. He affirmed the conclusions of the tentative opinion and made addition points in his final ruling on Tuesday. Netflix has indicated it is likely to appeal.
Netflix said: "As Judge Gross ruled, Fox failed to prove it was hurt in any way when two executives decided to exercise their right to go to Netflix. Fox's illegal contracts force employees to remain trapped in jobs they no longer wish to do and at salaries far below market rate. We will continue to fight to make sure that people who work in the entertainment industry have the same rights as virtually every other Californian and can make their own choices about where they work."
Advertising

If Logged Into Facebook, Oculus VR Data Will Now Be Used For Ads (uploadvr.com) 36

"Facebook will now use information about your Oculus activity, like which apps you use, to help provide [...] more relevant content, including ads" -- assuming you've connected your Oculus ID to your Facebook account. UploadVR reports: The company is updating its privacy policy and rolling out new social VR features backed by your "Facebook identity" with the intention of "clarifying how Oculus data is shared with Facebook to inform ads when you log into Facebook on Oculus." "These changes won't affect third-party apps and games, and they won't affect your on-device data," according to the company. For years now, buyers of Facebook VR headsets needed an Oculus ID to operate the system that could be optionally connected to your "Facebook identity" -- in other words, you could connect the two accounts. More recently, to access certain features like concerts in Venues, Facebook started requiring the use of the Facebook account. According to the company's terms, this account "must ... use the same name that you use in everyday life."

With this most recent change "If you choose not to log into Facebook on Oculus, we won't share data with Facebook to allow third parties to target advertisements to you based on your use of the Oculus Platform," according to Facebook. But denying that connection may also make it difficult to connect with others using virtual reality on Oculus systems. [...] Facebook suggests that for those who log into the account it will target "relevant content" based around "Oculus activity" including "which apps you use" with examples given including "Oculus Events you might like to attend or ads for VR apps available on the Oculus Store." The company says this "won't affect your on-device data" which, based on our previous reporting, Facebook says is the location where "3D maps of your environment" are kept. "We don't collect and store images or 3D maps of your environment on our servers today -- images are not stored anywhere, and 3D maps are stored locally on the headset [for Quest] and on your local PC, where you have access to delete it [for Rift S]," a Facebook representative originally wrote in an email.
Facebook also says the changes "won't affect third-party apps and games" and "if you choose not to log into Facebook on Oculus, we won't share data with Facebook to allow third parties to target advertisements to you based on your use of the Oculus Platform."
The Courts

ACLU is Suing ICE For Details on How It Uses Phone Spying Devices (cnet.com) 14

The American Civil Liberties Union filed a lawsuit Wednesday demanding that two US Homeland Security agencies -- Customs and Border Protection and Immigration and Customs Enforcement -- release details on how they've been using powerful phone surveillance tools. From a report: The ACLU is suing after the two agencies declined to provide it with documents related to International Mobile Subscriber Identity, or IMSI, catchers, more commonly known as Stingrays. These devices pretend to be cell towers and connect with nearby phones, intercepting data that details calls, messages and device location. IMSI catchers can often pull in data from entire neighborhoods, and they're able to obtain sensitive details on people without the people even knowing. Civil liberties and privacy groups have criticized the technology for its invasive surveillance. The two agencies have denied the ACLU's requests for information since 2017, telling the civil rights organization that "no records responsive to your request were found." The assertion comes despite the fact that a House Oversight Committee investigation in 2016 found that ICE spent $10.6 million on 59 IMSI catchers and that CBP had spent $2.5 million on 33 IMSI catchers.
Privacy

India Proposes New Rules To Access Its Citizens' Data (techcrunch.com) 14

India has proposed groundbreaking rules, akin to Europe's GDPR, that would require technology companies to garner consent from citizens before collecting and processing their personal data. But at the same time, the new rules also state that companies would have to hand over "non-personal" data of their users to the government, and New Delhi would also hold the power to collect any data of its citizens without consent to serve sovereignty and larger public interest. From a report: The new rules, proposed in nation's first major data protection law dubbed "Personal Data Protection Bill 2019," a copy of which leaked on Tuesday, would permit New Delhi to "exempt any agency of government from application of Act in the interest of sovereignty and integrity of India, the security of the state, friendly relations with foreign states, public order." If the bill passes select controversial laws drafted more than a decade ago would remain unchanged. The bill might also change how global technology companies that have invested billions of dollars in India, thanks in part to the lax laws, see the nation of more than 600 million internet users.
Links

The Pirate Bay Is Trialing High-Quality Video Streaming Links (torrentfreak.com) 35

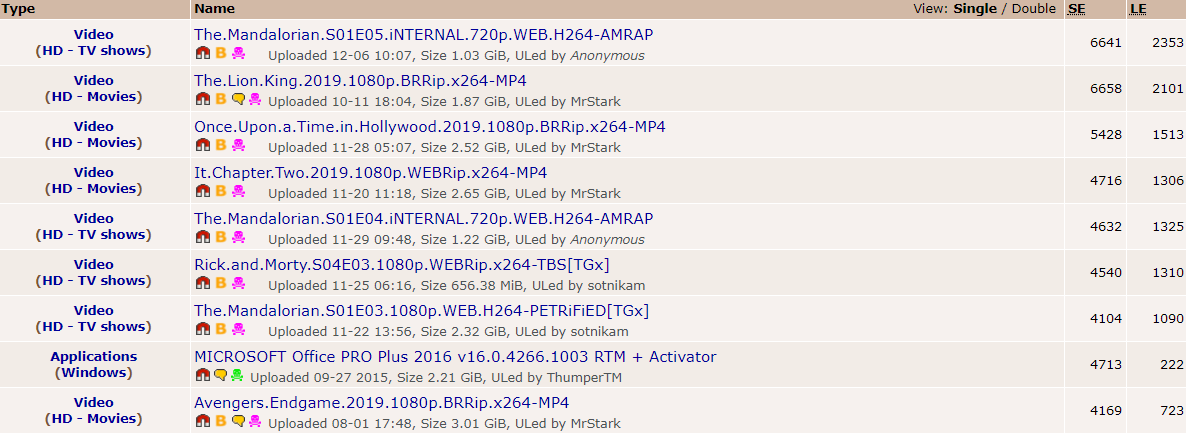
The Pirate Bay may be about to fully launch a brand new feature that will let you stream videos in your browser. TorrentFreak reports: As the image below shows, in addition to the familiar magnet and trusted uploader icons displayed alongside video and TV show releases, the site also features a small orange 'B' graphic. In some cases (but currently not all), pressing these buttons when they appear next to a video release diverts users to a new platform called BayStream. Here, the chosen content can be streamed directly in the browser using a YouTube-style player interface.

Loading times appear swift when the content is actually available and as the screenshot below shows, the material appears to be sourced, at least in some cases, from torrent releases. The new feature appears to be in its early stages of development and in tests doesn't always perform as planned. In particular, accessing the 'B' links using various Pirate Bay 'proxy' sites can cause them to break with various errors. Nevertheless, when things go to plan (usually when selecting more popular content) the system appears effective. [...] The big question, perhaps, is whether this is a Pirate Bay-operated platform or one run by outsiders. The familiar 'Kopimi' logo at the bottom suggests that it could be someone who supports the 'pirate' movement but anyone can use the image freely, so that's not the best pointer.

Chrome

Chrome Now Warns You When Your Password Has Been Stolen (theverge.com) 49

Google is rolling out Chrome 79, and it includes a number of password protection improvements. The Verge reports: The biggest addition is that Chrome will now warn you when your password has been stolen as part of a data breach. Google has been warning about reused passwords in a separate browser extension or in its password checkup tool, but the company is now baking this directly into Chrome to provide warnings as you log in to sites on the web.

You can control this new functionality in the sync settings in Chrome, and Google is using strongly hashed and encrypted copies of passwords to match them using multiple layers of encryption. This allows Google to securely match passwords using a technique called private set intersection with blinding. Alongside password warnings, Google is also improving its phishing protection with a real-time option. Google has been using a list of phishing sites that updates every 30 minutes, but the company found that fraudsters have been quickly switching domains or hiding from Google's crawlers. This new real-time protection should generate warnings for 30 percent more cases of phishing.

Censorship

Iran's Internet Freedom is On Life Support (cnet.com) 60

An anonymous reader shares a report: In November, Iran's government announced a price hike on oil, leading to mass protests in Tehran. To quell the spreading unrest, the Iranian government effectively shut down the internet. After a week of Iranian security forces cracking down on protesters, including an estimated death toll between 140 and 208, internet access was gradually restored around the country. Judging by statements made by President Hassan Rouhani, the internet shutdowns could be a harbinger of more censorship in 2020 and beyond. Iran's intranet, known as the National Information Network, will be expanded so "people will not need foreign [networks] to meet their needs," President Rouhani said to Iran's parliament on Sunday, according to Radio Farda. The decree to bolster the NIN comes from Supreme Leader Ali Khamenei himself, Rouhani said. Developing a more robust intranet would allow the Iranian government to cut access to the internet, and Iranians off from the rest of the world, without the economic self-impairment that internet cutoffs cause. An intranet would allow the Iranian government to select what sites and content Iranians can see, as opposed to the blunt and costly tool of a total shutdown.

Slashdot Top Deals